
Proof of review
for AI-generated code
AI writes code in seconds. But “correct” isn’t defined until someone writes it down. Signum turns every task into a contract, implements against it, audits with 3 independent models, and produces a tamper-evident proofpack.
The problem
A single model reviewing its own output is a self-audit. Your manual review is too shallow. Bugs slip through. There is no proof the code was actually checked.
3 verdicts, zero ambiguity
- AUTO_OK Safe to commit
- AUTO_BLOCK Regression found
- HUMAN Needs your review
How it works
Four phases, one approval gate
You approve the contract. Everything after that is autonomous.
Phase 1
Contract
Task decomposed into goal, scope, acceptance criteria, and hidden holdout scenarios. Spec scored A–F. Grade D is a hard stop.
You approve here
Phase 2
Execute
Engineer implements against the contract. Scope gate blocks out-of-scope changes. Execution policy constrains allowed tools and commands.
Autonomous
Phase 3
Audit
Claude, Codex, and Gemini review the diff independently. Holdouts run blind. Iterative fix loop — up to 20 rounds.
Autonomous
Phase 4
Pack
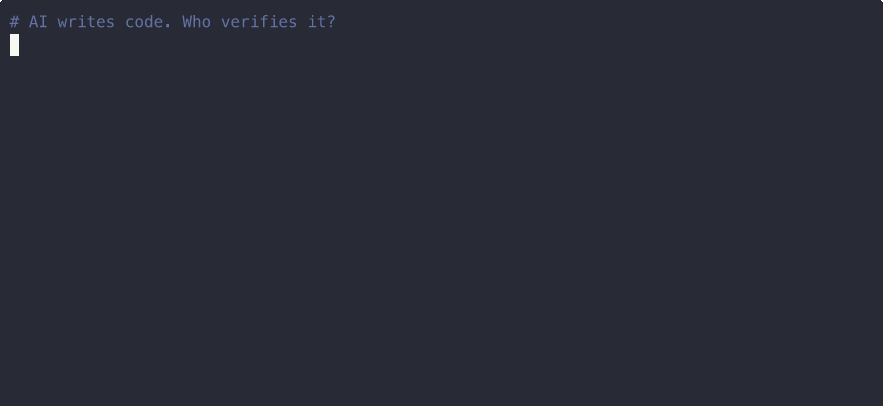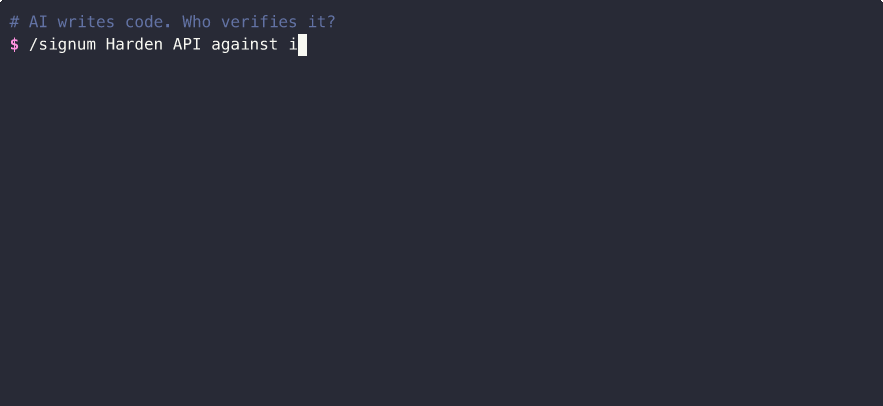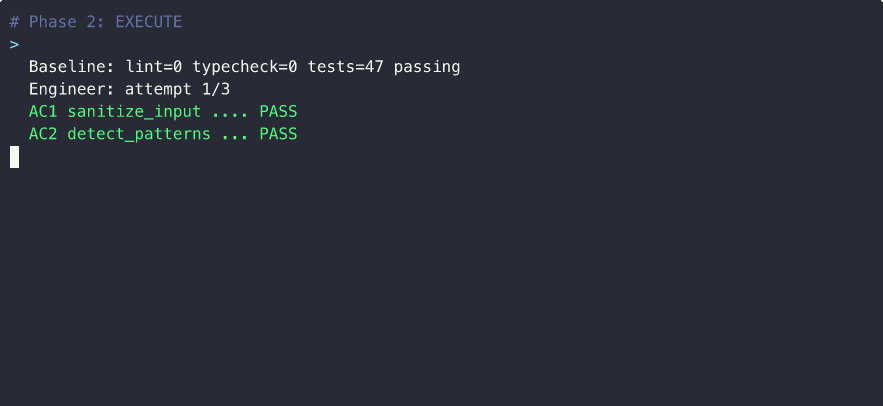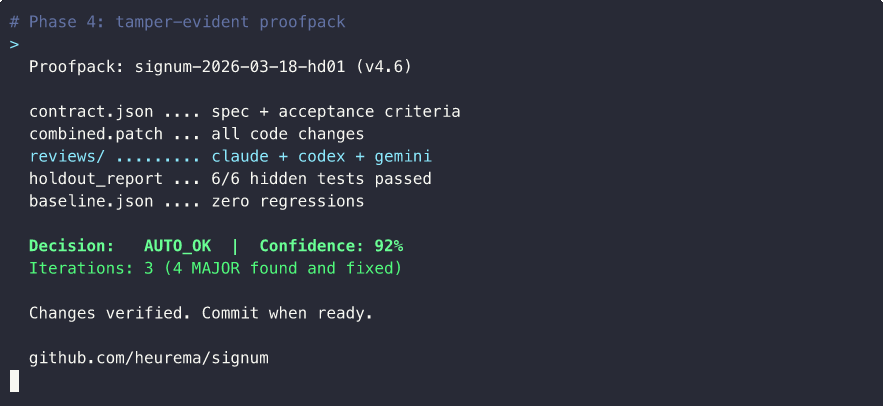
All artifacts bundled into a tamper-evident proofpack with SHA-256 chain from contract to verdict.
Autonomous
Features
Not another AI reviewer
Signum is proof of review — a signed attestation that AI-generated code was verified. Compliance gate, not reviewer replacement.
Holdout blinding
Tests the Engineer never sees
Hidden acceptance criteria are physically removed from the implementation contract. After coding, holdouts run as blind validation. The implementing agent cannot game them.
Multi-model audit
Three models, adversarial isolation
Claude reviews semantics, Codex reviews security, Gemini reviews performance. Each sees only goal + diff. A critical finding from any model triggers AUTO_BLOCK.
Proofpack
Tamper-evident artifact
Contract hash → approval timestamp → base commit → diff → audit results. Single proofpack file with per-artifact SHA-256 envelopes.
Iterative fix loop
Up to 20 repair rounds
When findings appear, the pipeline loops: repair → re-audit → repeat. Parallel repair lanes try different strategies. Best-of-N selection.
Spec quality gate
Grade D = no code written
Contracts scored A–F across 7 dimensions: testability, negative coverage, clarity, scope, completeness, boundaries, NL consistency.
Policy scanner
Zero-cost security scan
Deterministic scan on the diff for 12 security patterns: eval, XSS, SQL injection, weak crypto. CRITICAL findings trigger AUTO_BLOCK before any model runs.
In action
One command, full pipeline
Run /signum with a task description.
Approve the contract. Come back to a verdict and a proofpack.
For teams and solo devs
Setup call
30 minutes. I install Signum in your project, configure risk levels, run it on one of your PRs live, and walk you through the proofpack. You keep the full audit trail.
- Signum installed and configured for your repo
- Live audit on your real PR — you see the full pipeline
- Proofpack walkthrough — what each section means, how to use in CI
$99
30 min · 1-on-1 · your codebase
Book nowOr reply in the GitHub Discussion with a PR link — I’ll audit it for free.
Under the hood
Uses your existing AI subscriptions
Signum is a free, open-source Claude Code plugin. It runs on your own API subscriptions — Anthropic (required), plus OpenAI and Google for multi-model audit (optional).
Anthropic
Claude Code subscription. Required. Powers the pipeline core.
OpenAI
Codex CLI. Optional. Adds security-focused review.
Gemini CLI. Optional. Adds performance-focused review.
External providers receive only the goal and diff. Never the full codebase. No telemetry.
Get started
Install in 30 seconds
Via Claude Code CLI
claude plugin install signum@emporium Via nex
nex install signum Then run
/signum "Add a health check endpoint" Requirements
- claude-code v2.1+
- git, jq, python3
- codex + gemini CLI (optional)
Privacy
External providers receive only goal + diff. Never the full codebase.
No telemetry. All artifacts stay in .signum/.
Ship AI code with proof
Signum is shipping new capabilities: CI merge gates, audit dashboards, team compliance reports. Get notified when they land.
No spam. Unsubscribe anytime.
MIT licensed · heurema/signum